Linode.com, where this site is hosted, suffered a distributed denial of service attack this morning. It looks like my two blogs were down and flaky for about 2 hours but things are in hand now and back to normal again! Phew.
Mac OS X – how to update /etc/hosts
Way back in the good old days of Linux and Windows it was much easier to update my hosts file. There it was, /etc/hosts or C:\windows\hosts, edit, save and the change becomes active.
MacOS X is a little more complicated. Once you update /etc/hosts you’ll have to update the Netinfo Database. That’s why I’m blogging this so I’ll remember it. This page documents the steps required but the important command is this one:
sudo niload -v -m hosts . < /etc/hosts
There is a GUI but it’s a little clunky and duplicating an existing entry isn’t the most elegant method of adding a new one. Especially when a warning dialog pops up!
Thanks Barry for suggesting a similar fix while I was in SF and getting used to my new laptop! 🙂
Help protect the kids on busy roads
There was a knock at the front door a few minutes ago. That’s not something that happens very often during working hours. At the door was a teenager in school uniform with what looked like a notepad in hand. He was collecting signatures for a petition to have more zebra and pelican crossings built in Tower and Blarney.
The petition was set in motion by the death of Clodagh Murphy in a road accident on September 20th last. She was only 14.
Hopefully we’ll see some positive results from the petition but it’s going to involve education too. There’s a pelican crossing on the main road in Blarney. It’s a very busy road with several junctions leading onto the road in less than a few hundred meters distance. There’s also a bus stop on one side of the road, and a school on the other.
- I saw a teenager standing ready to run across the road. He was waiting for a break in traffic. He was right next to the pedestrian lights.
- Every morning over a dozen students pile out of the bus and go to the back of the bus. They too ignore the nearby pedestrian lights and by weight of numbers force the traffic to stop and walk across the road. I’ll have to get a picture of that some morning.
The mind boggles.
Ping Google Too!
Google announced that they will accept pings to their blogsearch service. Hopefully Pingomatic will support it soon so you don’t need to update your “Update Services” in WordPress. I’d say Matt’s sleeping off the jet lag from his trip to Vienna but it’ll probably be there in a few hours!
If you can’t wait, add “http://blogsearch.google.com/ping/RPC2” to the “Update Services” in your WordPress Dashboard under Options->Writing.
Why is this good? By pinging Google you can tell them that you have updated your blog. That will get your post into the Google Blog Search index that much faster.
Update! Matt has already updated Pingomatic. WordPress users can rest easy that their posts will show up quickly on Google Blog Search now!
Ryanair 0wn Aer Lingus
Ryanair are making a bid for Aer Lingus! The former national carrier, Aer Lingus, went public a few days ago. Ryanair snapped up 16% of the company and are now offering “an all cash offer of €2.80 per share.”
I can just imagine the gnashing of teeth of Aer Lingus employees as they contemplate the cuts and cost savings Michael O’Leary would introduce!
Killing off PHP
Do you know why Apache processes get stuck and stop responding when serving pages on a WordPress site?
I’ve seen this happen here and on my previous host on a regular basis. I don’t know what happens. It can’t be a PHP script gone into an infinite loop because the normal Apache timeout should kill it. It’s not MySQL as a quick inspection of the process list usually shows it’s empty.
It could be plugins, some of them haven’t been written to the high standards that is expected in WordPress core. It could be some strange interaction between plugins and core code and memory limits and PHP extensions.
Whatever causes it, this will fix it. It’s brutal, it’s crude, but it’ll stop the load average going up on your box and it will ensure that every Apache child process is listening and responding. Add this to the crontab of your nobody or www-data user. Pick whichever user runs the webserver because you want to limit the damage in case something bad happens and the command malfunctions!
*/10 * * * * ps auxw|grep apache2| awk '$10 !~ /0:00/ {print $2":"$10}'|awk -F ':' '$2 !~ 0 {print $1}'|xargs kill -9 2> /dev/null
What this does is it uses the ps, grep, and awk tools to find processes that are using anything more than the minimum CPU time. It is very crude, but it works.
If you use Litespeed, then replace “apache2” with “lsphp”. I have found that this is very necessary as those processes get stuck quite often, especially in low memory situations.
Where's the evil in top posting?
Where is the evil in top posting when replying to a message on a mailing list? It’s something I’ve never understood, even after reading the many “why top posting is evil” posts and FAQs around the interweb.
Inspired by yet another email complaining about a top post to the GIMP mailing list I briefly searched Google, the source of all information in the world, and found this enlightening page on the evils of top-post complaints.
Regardless, top-posting flame wars are always fun to watch from the sidelines. People on both sides of the arguement will fight for their own side in what is a subjective matter and way of writing. Flame away!
Live from BarCamp Ireland
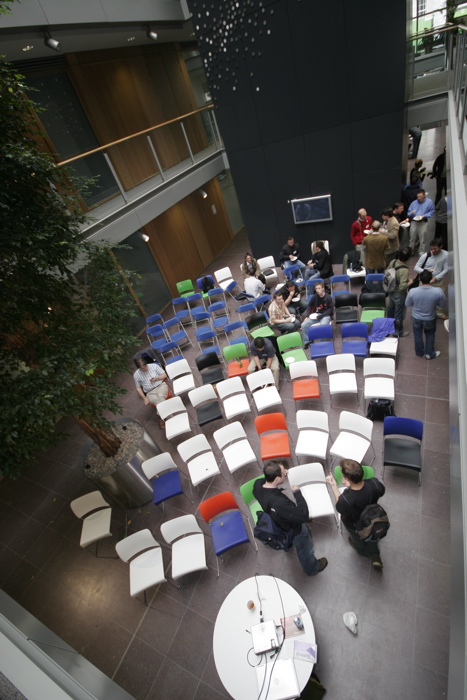
Here we are, live from BarCamp, predictably I’m late, but just in time for lunch!
I'll be there too
See you tomorrow at BarCamp Ireland! There’s going to be a big crowd and great speakers. Tom will be there and he has volunteered to speak twice. I won’t be talking, but come up to me and ask me about WordPress MU and wordpress.com, I’ll be the one wearing the WordPress tshirt!
I see that the wiki has been updated with the following message:
All attendees, whether you have signed up already or not, please send your contact email address to barcampireland at gmail dot com. Thanks.
It’s a public wiki and I haven’t seen the same message on the BarCamp Ireland Blog so maybe hold off sending that email until there’s a similar announcement tomorrow. Me paranoid? Never!
While I’m here, blogging at 23:30, this will be of interest to the rest of Automattic and anyone else who works at home – Myths About Working From Home. You never really leave the job do you? (via)
Drowning in the flood
I have noticed a strange thing in the past week or so. Google has referred legitimate looking browser user agents to this blog and In Photos.org and within seconds that browser tries to download all my feed links, and several months of my archives. I have a little flood protection built in and it stops them with a 403 after several of these requests but it’s annoying. It’s some sort of pre-fetching plugin to “speed up” browsing isn’t it? Firefox has a similar thing in the form of the “Fasterfox” extension if memory serves. Ben Metcalfe has a good write up on the evils of pre-fetching. It could kill your database or use all your credits in online stores!
Whatever you’re using, welcome to my kill file.
64.136.27.227 … “GET /index.php?tag=suicide-girls HTTP/1.1” 200 36422 “http://www.google.com/search?q=suicide+girls&hl=en&lr=&start=20&sa=N” “Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 1.1.4322)”
64.136.27.227 … “GET /wp-content/plugins/widgets/rss.png HTTP/1.1” 200 3341 “https://inphotos.org/index.php?tag=suicide-girls” “Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 1.1.4322)”
64.136.27.227 … “GET /feed/atom/ HTTP/1.1” 200 35775 “https://inphotos.org/index.php?tag=suicide-girls” …
64.136.27.227 … “GET /feed/ HTTP/1.1” 200 35449 …
64.136.27.227 … “GET /feed/rss/ HTTP/1.1” 200 4636 …
64.136.27.227 … “GET /wp-content/themes/whiteasmilk/style.css HTTP/1.1” 200 9639 “-” …
64.136.27.227 … “GET /xmlrpc.php HTTP/1.1” 200 42 …
64.136.27.227 … “GET /2006/07/ HTTP/1.1” 200 68150 …
64.136.27.227 … “GET /2006/09/ HTTP/1.1” 200 68150 …
64.136.27.227 … “GET /2006/08/ HTTP/1.1” 200 68150 …
64.136.27.227 … “GET /2006/06/ HTTP/1.1” 200 68150 …
…